Threat Insight
CVE-2026-104286: FortiMail Path Traversal Vulnerability Actively Exploited
Fortinet has disclosed a critical vulnerability affecting FortiMail that is being actively exploited in the wild. The vulnerability, tracked as CVE-2026-104286, is a path traversal flaw combined with improper neutralization of NULL byte characters that may allow an unauthenticated attacker to write arbitrary files to the underlying operating system via crafted HTTP or HTTPS requests.
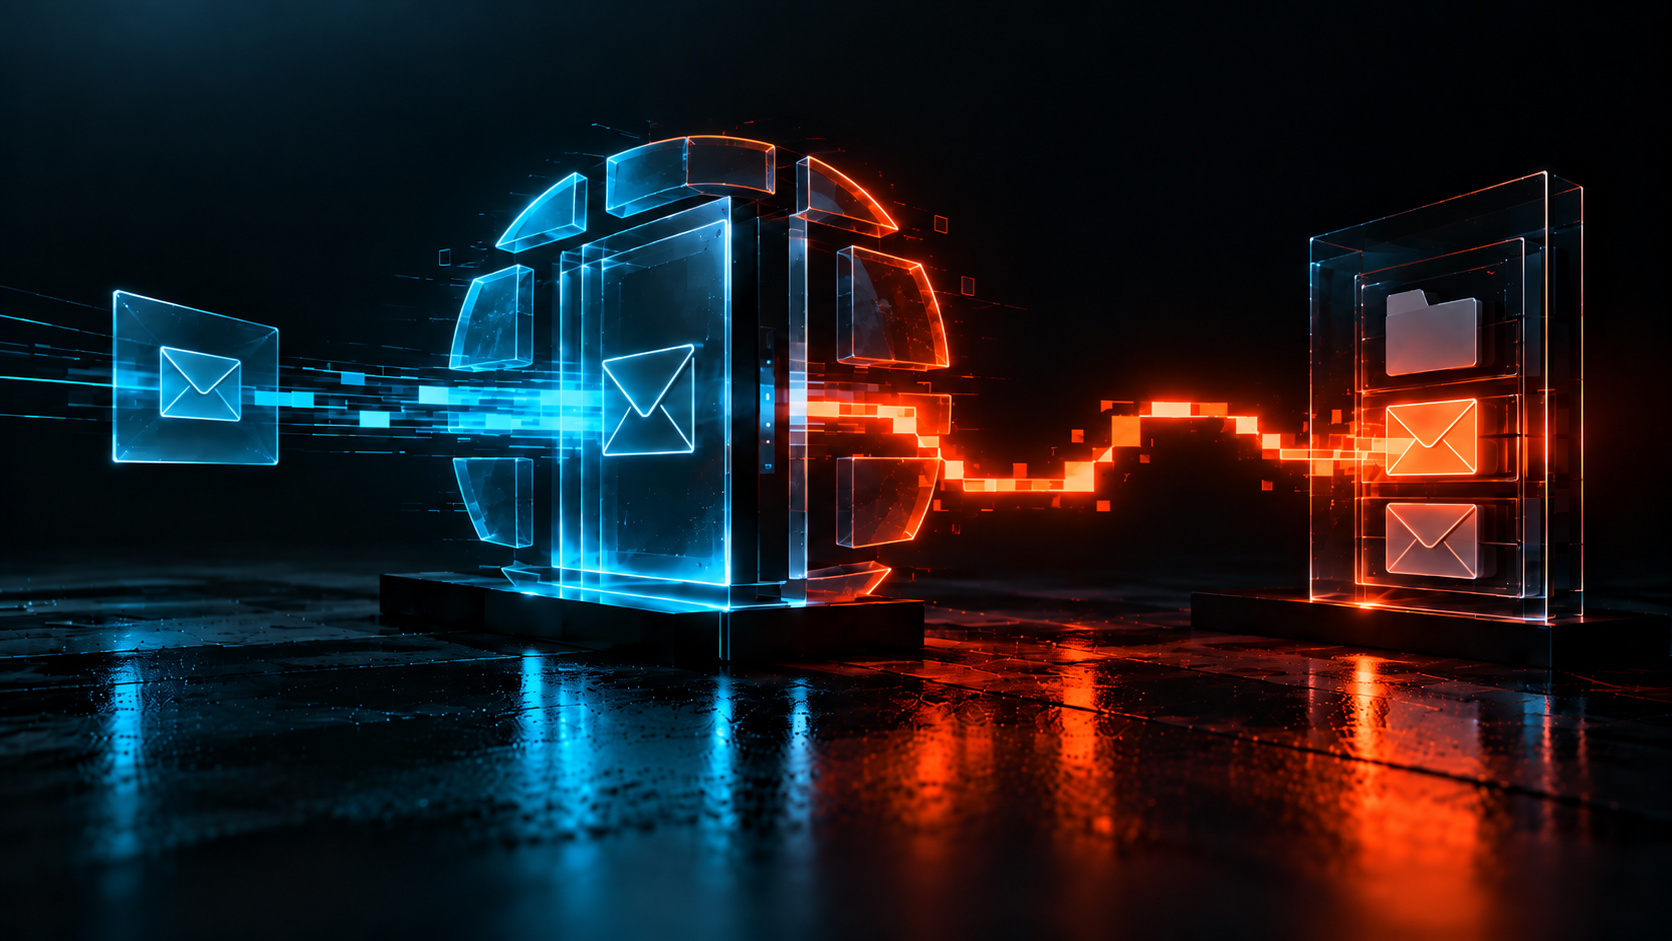
Successful exploitation may let an unauthenticated attacker send a crafted request that tricks FortiMail into writing a file outside its intended folder.
By placing a file onto the underlying system, the attacker gains a way to run commands on the device itself. This can lead to full control of the mail gateway, exposing stored mail, credentials, and other systems it connects to.
CVE
CVE-2026-104286
Affected Products
FortiMail 8.0 through 8.0.1
FortiMail 7.6 through 7.6.6
FortiMail 7.4 through 7.4.8
FortiMail 7.2 through 7.2.9
Exploitation
The vulnerability has been exploited in the wild[1].
Recommended Actions
Currently there are no patches available, here are the current workaround as provided by Fortinet’s PSIRT[1]:
- Disable the IBE feature support using the following CLI command:
config system encryption ibe set status disable end - Alternatively: Disable access to the FortiMail management interface from the internet or limit the access only from trusted private network
Detection
Logs[1]:
type=event subtype=system pri=debug user=system ui=cron msg="(root) CMD (/bin/sh -c 'O=/migadmin ...type=kevent subtype=admin pri=information user=admin ui=(null) action=logout status=success reason=unknown msg="User admin logged out from (null)."type=kevent subtype=config pri=information user=admin ui=cli module=unknown submodule=unknown msg="Added 'archive234' to 'archive account' : rotation-size[50]rotation-time[1] rotation-hour[14]destination[remote]remote-ip[79.141.169.187]remote-username[archive234]remote-password[***]remote-directory[/uploads] (user: admin, from: cli)"FortiMail::IBE::DecrypterMediaIn::DecrypterMediaIn(FortiMail::MediaIn&, const FortiMail::IBE::KeyFinder&, const FortiMail::EmailAddress&, const FortiMail::Buffer&, FortiMail::IBE::DecrypterMediaIn::Version): Caught BufferException(2), BufferImpl.cpp:973, 'Invalid Base64 Encoding at pos 0. Character=0x2a'Internal user *@domain.tldmailto:*@domain.tld failed to log in.
Truesec has added the below IOCs to Automated Hunting, these will be hunted for every 4th hour across all EDRs.
Files[1]:
- [ADDED]/data/lib/liblog.so MD5 – 64c90a00c7fda4d5c7973ed64c25783a SHA256 – 8015f34dc84922b03688399d7f9fe7a00361789f7e420c7e2a2cdb23e75cef84
- [MODIFIED]/bin/smit MD5 – 5241738a3e9988404239e12243f6d35b SHA256 – 77324ac428bde86d351fc5fc06f6d64a6bfe737dfb2743df1d4c5ac2418a5b6a
- [ADDED]/data/bin/webconsole MD5 – ae0ea6502d3fa5f0664bceb73189eb54 SHA256 – 7a6cea9f5c9e2e9994d4e3c4da73f86cf5acd05ea5d312c066c9d1dafd69ee38
- [ADDED]/data/bin/mailservice MD5 – f90fa81a5f521d785f2b2f765e3ab897 SHA256 – 4000276a150a165d3c2537d1e19fb393c4de8333076a16655e28059cae82157b
- [MODIFIED]/data/etc/httpd.conf MD5 – 61af1c4bce1c2eebc8ff689ca5337791 SHA256 – 703e97c64e61e41dc3aaba580d82bb2aa7b6a11b54ee6fb467ed5d5a3bffdef5
- [ADDED]/data/etc/ld.so.preload MD5 – 8eb64f25d2a8e18e05aae058629473cf SHA256 – 8953ec7960b09f544a880b072ad4e6cfda7a8303f486251d3478dcfdfbac23b6
- [MODIFIED] /data/migadmin.tar.gz MD5 – 49a7156a7d043cc8f9f680579db22f86 SHA256 – d6fe51c22b91776f4c961ea58bcac5917f15d560a619d7ce726d3d51795609d3
IPs[1]:
79[.]141.169.187
45[.]129.0.192
References
Stay ahead with cyber insights
Newsletter
Stay ahead in cybersecurity! Sign up for Truesec’s newsletter to receive the latest insights, expert tips, and industry news directly to your inbox. Join our community of professionals and stay informed about emerging threats, best practices, and exclusive updates from Truesec.
Your current browser privacy settings may be preventing this form from loading properly. To continue, please allow cookies/tracking for this site or temporarily disable strict privacy protection, then refresh the page.
If you’re still experiencing issues, please contact us at hello@truesec.com
Latest Insights

CVE-2026-85706: Critical GitLab Unauthenticated Arbitrary File Read Vulnerability (CVSS 10.0)
Danish SAMSIK and Defence Intelligence Services Raises Threat Level For Destructive Cyberattacks